

Microsoft ISOC explained: what it is, who it is for, and how it compares to Sentinel
On September 23, Microsoft announced the Integrated Security Operations Center, or ISOC, in Microsoft Defender. My LinkedIn feed…

AI playbook generator in Microsoft Sentinel: turn a sentence into working SOC automation
Every SOC lead has the same automation backlog problem. There is a long list of response actions everyone…
BYOVD is back: how EDR killers ship inside RaaS kits and how to stop them
If you have been reading ransomware incident reports over the past few months, you have probably noticed the…
MDTI convergence: threat intelligence now built into Defender and Sentinel
The final phase of the Microsoft Defender Threat Intelligence (MDTI) convergence went generally available in the Defender portal…
AI agent runtime protection in Microsoft Defender for Endpoint
Discovery tells you an agent exists. It doesn’t tell you when someone tries to hijack it. That’s the…
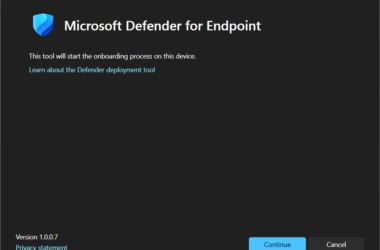
Defender deployment tool: Easy and simple onboarding for Defender for Endpoint
Onboarding devices to Microsoft Defender for Endpoint has always been one of those tasks that looks simple on…
Microsoft Defender for Endpoint custom data collection: get the telemetry you need
If you’ve been working with Microsoft Defender for Endpoint (MDE) for any length of time, you’ve probably run…
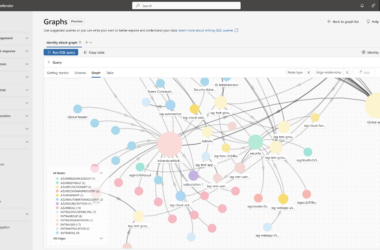
Identity attack graph in Microsoft Sentinel: easy find lateral movement paths
Sentinel graph ships with two layers. One is custom graphs, where you build your own schema from any…
Getting started with OpenCTI: threat intelligence connected to Microsoft Sentinel
For the past few years, MISP has been my go-to for threat intelligence. It’s open source, flexible, and…
Microsoft Defender for Identity sensor guide (v3.x)
In a previous post on modernsecurity.nl, I walked through the classic installation of Microsoft Defender for Identity (MDI)…