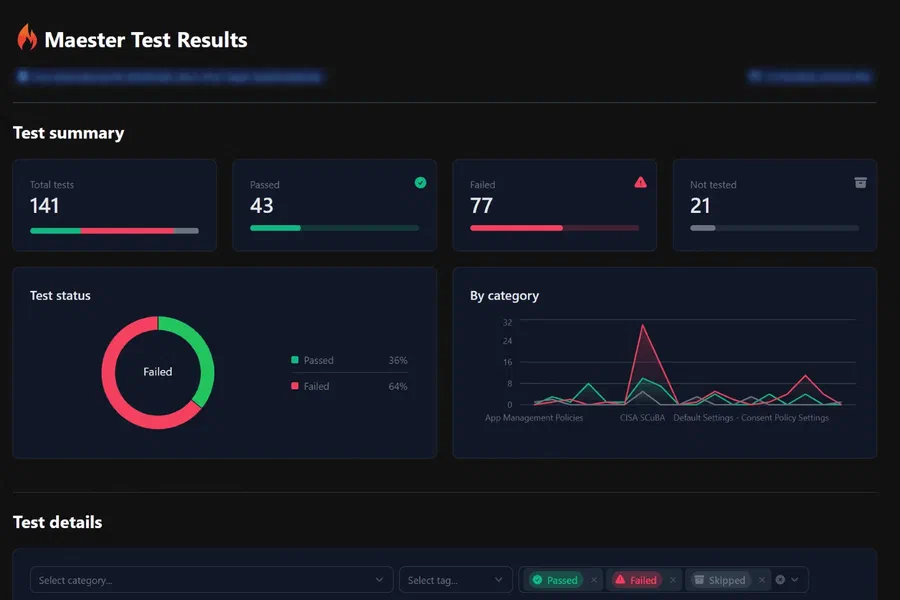
Maester – Swiss army knife for M365 security testing
Discover Maester: automate Microsoft 365 security with tests, alerts, and reports. Ensure compliance, enhance security, and stay proactive in your tenants.
8 minute read
Modern Security is free and ad-free. If an article saved you time, you can buy me a coffee to keep the guides coming.
Buy me a coffeeFollow Modern Security
Technical perspectives on security compliance, NIS2, governance, and translating Microsoft security capabilities into compliant architectures.
Security compliance is most effective when it is built on solid technical foundations rather than policy alone. This category focuses on bridging the gap between regulatory requirements and technical security controls, with a strong emphasis on Microsoft-based environments.
Articles in this section explore how frameworks such as NIS2, ISO standards, and governance models translate into concrete security capabilities. Rather than treating compliance as a separate discipline, the content highlights how detection, logging, identity protection, and exposure management support compliance objectives in practice.
You will find analysis on how Microsoft security solutions contribute to audit readiness, risk management, and continuous compliance, including logging strategies, monitoring depth, and architectural decisions that impact governance. The focus is on practical implementation choices, not just theoretical alignment.
This category is particularly relevant for security architects, consultants, and decision-makers who need to justify technical security investments in the context of compliance and regulatory pressure.
Discover Maester: automate Microsoft 365 security with tests, alerts, and reports. Ensure compliance, enhance security, and stay proactive in your tenants.
For a while, I managed several tech blogs, but due to time constraints, I had to let them go. Now, I'm eager to set one up again, focusing primarily on