As of Feb. 1, 2024, Google has announced that they are going to make some changes to their security guidelines in Gmail regarding email senders. How exactly they are going to implement this is not 100% clear yet because this policy only applies to companies that send more than 5,000 emails per day to Gmail.
But is this all of a sudden? And how does this affect other senders and recipients? Well, to be honest, this should have been in place already in your own environment for ages. With SPF, DKIM, and DMARC in place, you have standard hygiene established.
Regardless of the great options Microsoft and Defender for Office 365 offers, you can’t go around this standard hygiene. Microsoft also changed their advisory this month, to configure DMARC more strict and on all the domains you own. Yay \o/
But what does SPF, DKIM and DMARC mean and why do you need it?
In an era where digital communication is integral to our personal and professional lives, ensuring the authenticity of emails is paramount. Email, being a ubiquitous form of communication, is susceptible to various forms of abuse, including phishing, spoofing, and unauthorized tampering. To counter these threats, three essential email authentication protocols – SPF (Sender Policy Framework), DKIM (DomainKeys Identified Mail), and DMARC (Domain-based Message Authentication, Reporting, and Conformance) – have emerged as indispensable tools for bolstering email security.
Sender Policy Framework (SPF): SPF addresses the challenge of email spoofing by allowing domain owners to specify which mail servers are authorized to send emails on behalf of their domain. By publishing SPF records in DNS, organizations ensure that receiving mail servers can verify the legitimacy of the sending server, mitigating the risk of fraudulent emails bearing their domain.
DomainKeys Identified Mail (DKIM): DKIM adds a layer of integrity verification to emails by attaching a digital signature to the message. This signature, generated by the sending mail server’s private key, is verified by the recipient’s server using a public key published in DNS. DKIM ensures that the email has not been tampered with during transit and verifies the sender’s authenticity.
Domain-based Message Authentication, Reporting, and Conformance (DMARC): DMARC builds upon SPF and DKIM, providing a comprehensive policy framework for email authentication. With DMARC, domain owners can specify how unauthenticated emails should be handled, whether to monitor, quarantine, or reject them. DMARC also facilitates the receipt of detailed reports, enabling organizations to analyze and fine-tune their email authentication practices.
Why it’s needed: The need for robust email authentication mechanisms is evident in the face of escalating cyber threats. Without SPF, DKIM, and DMARC, malicious actors can exploit vulnerabilities, impersonate legitimate entities, and compromise the integrity of email communication. Implementing these protocols collectively establishes a multi-layered defense against phishing attacks, safeguards against unauthorized email transmission, and fosters a more trustworthy email ecosystem.As organizations embrace these email authentication standards, they not only protect their own reputation but also contribute to the overall improvement of global email security. In an interconnected digital landscape, SPF, DKIM, and DMARC stand as essential guardians, working together to fortify the foundations of secure and authentic email communication.
So…. but how does it work? And what do I need to setup?
SPF (Sender Policy Framework):
- Purpose: SPF is an email authentication protocol that helps prevent email spoofing and phishing by verifying that the sender’s email server is authorized to send emails on behalf of a specific domain.
- How it Works:
- When an email is sent, the receiving mail server checks the SPF record of the sender’s domain.
- The SPF record is a DNS (Domain Name System) record that specifies which mail servers are authorized to send emails on behalf of the domain.
- If the sending mail server is listed in the SPF record, the email is considered authentic; otherwise, it may be marked as suspicious or rejected.
- Implementation:
- Domain owners publish SPF records in their DNS settings.
- SPF records include information about the authorized mail servers and their IP addresses.
- Example SPF Record:
v=spf1 mx ip4:192.168.1.1 include:_spf.example.com -allThis record allows the domain’s MX servers, the specific IP address 192.168.1.1, and the servers listed in the _spf.example.com domain to send emails on behalf of the domain. For M365 the default SPF will be > include:spf.protection.outlook.com.
DKIM (DomainKeys Identified Mail):
- Purpose: DKIM is an email authentication method that adds a digital signature to the email message, allowing the recipient to verify that the email has not been tampered with during transit and that it was actually sent by the claimed sender.
- How it Works:
- The sending mail server generates a unique signature for each outgoing email using a private key.
- This signature is added to the email header as a DKIM-Signature field.
- The recipient’s mail server can then use the public key (published in the DNS) to verify the authenticity of the signature.
- Implementation:
- Domain owners generate key pairs (public and private) for DKIM (as for M365 you can find your DKIM keys here: https://security.microsoft.com/authentication > make sure to fix your SPF, DKIM and DMARC for every domain you own)
- The public key is added to the DNS as a TXT record.
- Example DKIM-Signature Field:
DKIM-Signature: v=1; a=rsa-sha256; d=example.com; s=selector; c=relaxed/simple; q=dns/txt; i=@example.com; t=1234567890; h=From:To:Subject:Date; bh=dahf1aJS6wLfW1zrV9j9q1ZZlaM=; b=d2k1TWAx1fvmB7Lc8d5vdoE2Yp0/uHb5p/hS9KVoTZv+uEv/YUkth8UgM R2Y2jhmtIkNvZ2i2Lxi0I3mLpHnSv9F2kK2+8SkH3FZwb/DcPCxhV+d3lE==This is a simplified example of a DKIM-Signature field, and it includes information about the cryptographic algorithm, the domain, the selector, and the signature itself.
DMARC (Domain-based Message Authentication, Reporting, and Conformance):
- Purpose: DMARC builds on SPF and DKIM to provide a policy framework for email authentication. It helps domain owners specify what actions to take on unauthenticated emails and allows them to receive reports on email authentication activity.
- How it Works:
- DMARC records are published in DNS and specify the policy for handling unauthenticated emails.
- DMARC policy options include monitoring (reporting only), quarantine (put in spam/junk folder), and reject (do not deliver).
- DMARC relies on the alignment of SPF and DKIM with the “From” address in the email header.
- Implementation:
- Domain owners publish DMARC records in their DNS settings
- Example DMARC Record:
v=DMARC1; p=quarantine; rua=mailto:dmarc@example.com; ruf=mailto:dmarc@example.comThis DMARC record specifies a policy of quarantine for unauthenticated emails and instructs the recipient’s mail server to send aggregate reports (rua) and forensic reports (ruf) to the specified email address. Please check Valimail if you’re in the need of a good DMARC reporting tool (https://www.valimail.com)
Overall Workflow:
- SPF verifies the sender’s server.
- DKIM verifies the integrity of the email’s content.
- DMARC evaluates the alignment of SPF and DKIM, and based on the specified policy, takes action on unauthenticated emails.
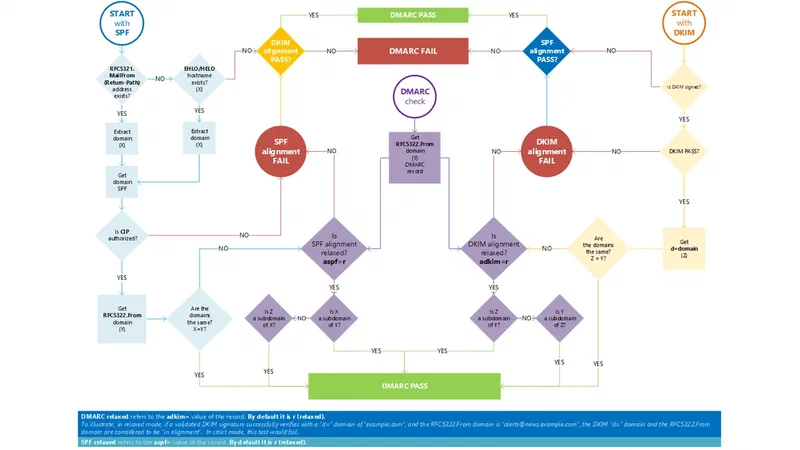
By implementing SPF, DKIM, and DMARC together, organizations can significantly enhance email security, reduce the risk of phishing attacks, and provide a more trustworthy email environment. Regular monitoring and analysis of DMARC reports can also help organizations fine-tune their email authentication settings and identify potential issues.
Comments
Comments need JavaScript to load.
Leave a comment
Comments are moderated and appear after approval. Plain text only; links are shown but not clickable.