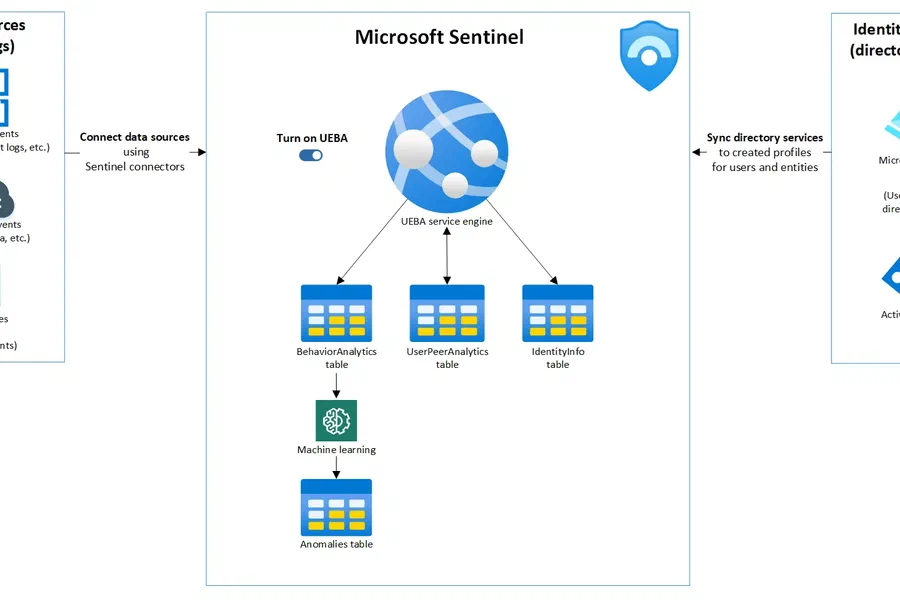
UEBA behaviors layer in Microsoft Sentinel: from raw logs to behavioral intelligence
Learn about the UEBA behaviors layer in Microsoft Sentinel. What it does, how to enable it, and use it for investigation and threat hunting.
7 minute read
Modern Security is free and ad-free. If an article saved you time, you can buy me a coffee to keep the guides coming.
Buy me a coffeeFollow Modern Security
Learn about the UEBA behaviors layer in Microsoft Sentinel. What it does, how to enable it, and use it for investigation and threat hunting.
Learn how to set up Microsoft Defender for Cloud Apps AI agent monitoring. Covers inventory, advanced hunting, and real-time protection.
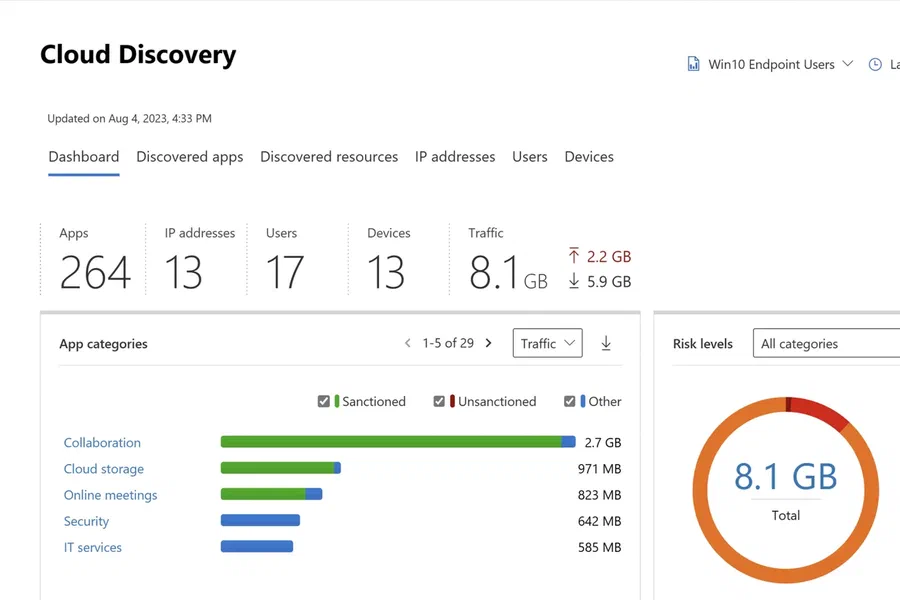
Learn how to block shadow IT and risky cloud applications (like AI apps) using Microsoft Defender for Cloud Apps with Defender for Endpoint.
Guide to implement Microsoft Sentinel data lake step-by-step, cost optimization, DCR transformation, advanced analytics and management.
Step-by-step guide to implementing Microsoft's Automatic Attack Disruption in Defender XDR, with all the configuration and products needed.
Use Microsoft Defender for Endpoint's Selective Isolation with Velociraptor to investigate compromised endpoints remotely, full DFIR without losing access.
Integrate Microsoft Defender EASM with Exposure Management to enrich attack paths with external risk data and strengthen your posture.
Learn how Microsoft Defender XDR automatically maps analytics rules to MITRE tactics and techniques using AI. Step-by-step guide with SOC examples.