Maximizing security with Microsoft Defender for Identity
Protect your organization’s identities with Microsoft Defender for Identity. Detect threats, improve security posture, and reduce attack surfaces effectively.
5 minute read
Modern Security is free and ad-free. If an article saved you time, you can buy me a coffee to keep the guides coming.
Buy me a coffeeFollow Modern Security
Every Modern Security article on Microsoft Sentinel, Defender XDR, Entra ID, identity security and SOC operations, newest first.
Protect your organization’s identities with Microsoft Defender for Identity. Detect threats, improve security posture, and reduce attack surfaces effectively.
Urgently detect and mitigate Active Directory threats. With this blog we take a look at the most common AD attacks and post how the hardening works.
Enhance security with Microsoft Defender for Endpoint (MDE) Deception. Detect threats early, and prevent lateral movement.
Microsoft deprecates NTLM, this post is about why and the importance of Kerberos. Also demonstrating how to easily crack NTLM hashes with Hashcat.
One of the key features of Microsoft Sentinel is the SOC Optimization capability, which is now in Public Preview. This feature makes it easier for
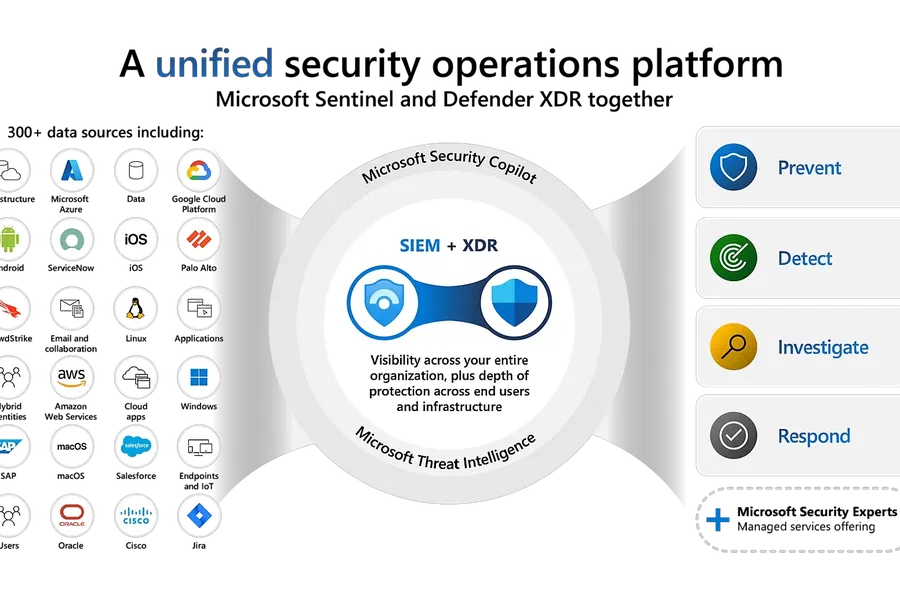
Check out the new Microsoft Unified Security Operations Platform. It combines the power of Microsoft Sentinel and Defender XDR, together in one.
Discover how Microsoft Security Exposure Management enhances threat prevention with real-time insights aligned to your organization's risks.
In this article, we’ll delve into the fundamentals of QR Code Phishing (Quishing) and provide actionable steps to safeguard against this threat.
Evilginx3 is a MiTM attack framework for phishing login credentials along with session cookies (MFA). In this blogpost used together with Gophish.
How do you setup SPF, DKIM and DMARC on your environment? And how does it help? Read about it here and make sure to follow us