Automatically tagging MITRE techniques with AI in SOC Optimization
Learn how Microsoft Defender XDR automatically maps analytics rules to MITRE tactics and techniques using AI. Step-by-step guide with SOC examples.
3 minute read
Modern Security is free and ad-free. If an article saved you time, you can buy me a coffee to keep the guides coming.
Buy me a coffeeFollow Modern Security
Every Modern Security article on Microsoft Sentinel, Defender XDR, Entra ID, identity security and SOC operations, newest first.
Learn how Microsoft Defender XDR automatically maps analytics rules to MITRE tactics and techniques using AI. Step-by-step guide with SOC examples.
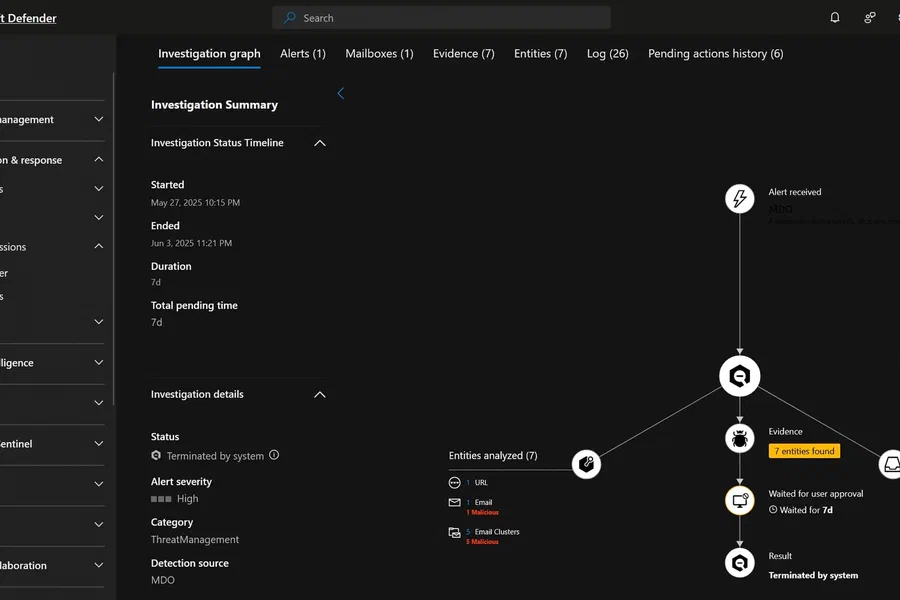
Enable Defender for Office 365 Auto‑Remediation to cut SOC dwell time and auto-delete threats. Learn how it works and how to monitor it.
Learn how to manage and block risky browser extensions using Microsoft Defender TVM, and Intune. Protect your users from modern browser threats.
Discover how to use Microsoft Case Management in Defender & Sentinel to streamline SecOps with real-world tips, steps, and best practices.
Learn how to investigate and secure OAuth apps in Microsoft 365 using Entra ID, Sentinel, Defender XDR, and App Governance to prevent consent phishing attacks.
Learn how to integrate T-Pot honeypots with AMA and Microsoft Sentinel using DCRs, visualize data and enhance threat detection with actionable insights.
Configure Microsoft Defender External Attack Surface Management (EASM) to reduce your organization's external risks, learn how by following this blogpost.
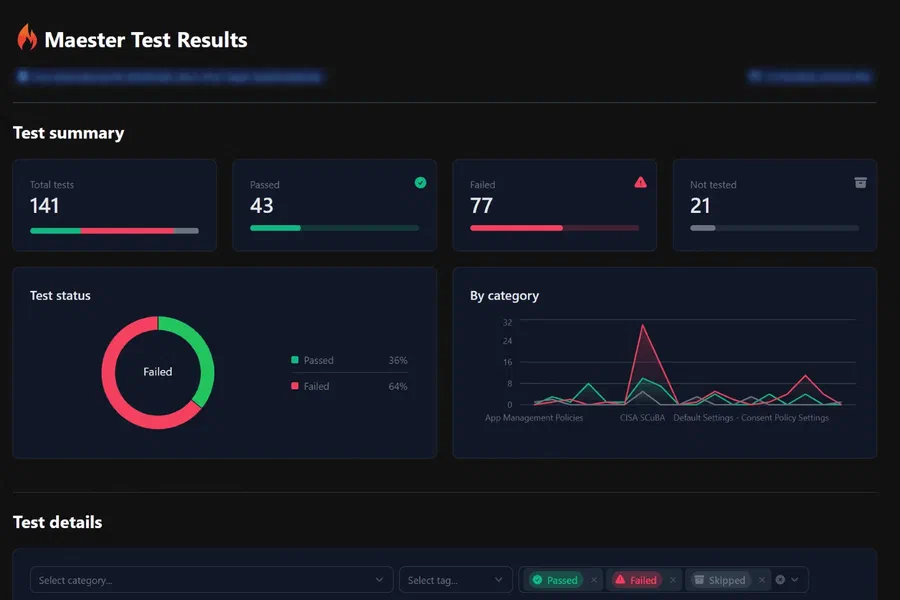
Discover Maester: automate Microsoft 365 security with tests, alerts, and reports. Ensure compliance, enhance security, and stay proactive in your tenants.
Discover how to effectively deploy, configure, and monitor honeytoken accounts in Microsoft Defender for Identity (MDI) to detect identity threats
Step-by-step guide to install and configure Microsoft Defender for Identity, ensuring optimal security and performance for your environment.