Why Modern Security left WordPress: rebuilding the blog with Hugo and Blowfish
Modern Security moved from WordPress to a static Hugo and Blowfish site on Cloudflare Workers. Why I did it, how the migration worked, and what changed for you.
Every Modern Security article on Microsoft Sentinel, Defender XDR, Entra ID, identity security and SOC operations, newest first.

Modern Security moved from WordPress to a static Hugo and Blowfish site on Cloudflare Workers. Why I did it, how the migration worked, and what changed for you.

Microsoft ISOC brings SIEM into Defender as an E5 and E7 benefit. What it is, who it's for, and what Sentinel customers should know.

Microsoft Sentinel AI playbook generator: turn a sentence into a working SOC automation, no SCU or Logic Apps needed.

BYOVD-based EDR killers are now offered in ransomware-as-a-service operations. Countermeasures with ASR, vulnerable driver blocklist, HVCI, and WDAC.

Microsoft Defender Threat Intelligence (MDTI) convergence reached GA. Step-by-step on the connector, using the Graph API, and what to check before.

How Microsoft Defender for Endpoint's AI agent runtime protection detects and blocks prompt injections before executing (now in preview)

Easy Microsoft Defender for Endpoint onboarding with Defender Deployment Tool: setup, command-line use, and rollout considerations.

Learn about how Microsoft Defender for Endpoint Custom Data Collection fixes lack of visibility, and step-by-step instructions to implement it properly.

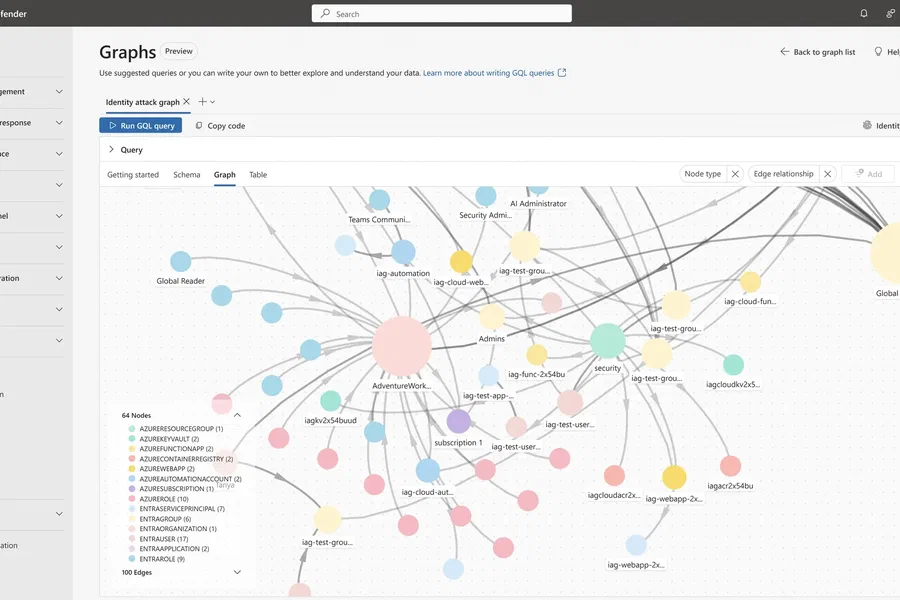
Map lateral movement paths across Entra and Azure. Step-by-step setup guide for the Microsoft Sentinel identity attack graph.

A practical guide to installing OpenCTI, adding threat intelligence feeds and connecting it to Microsoft Sentinel for enriching TI information.